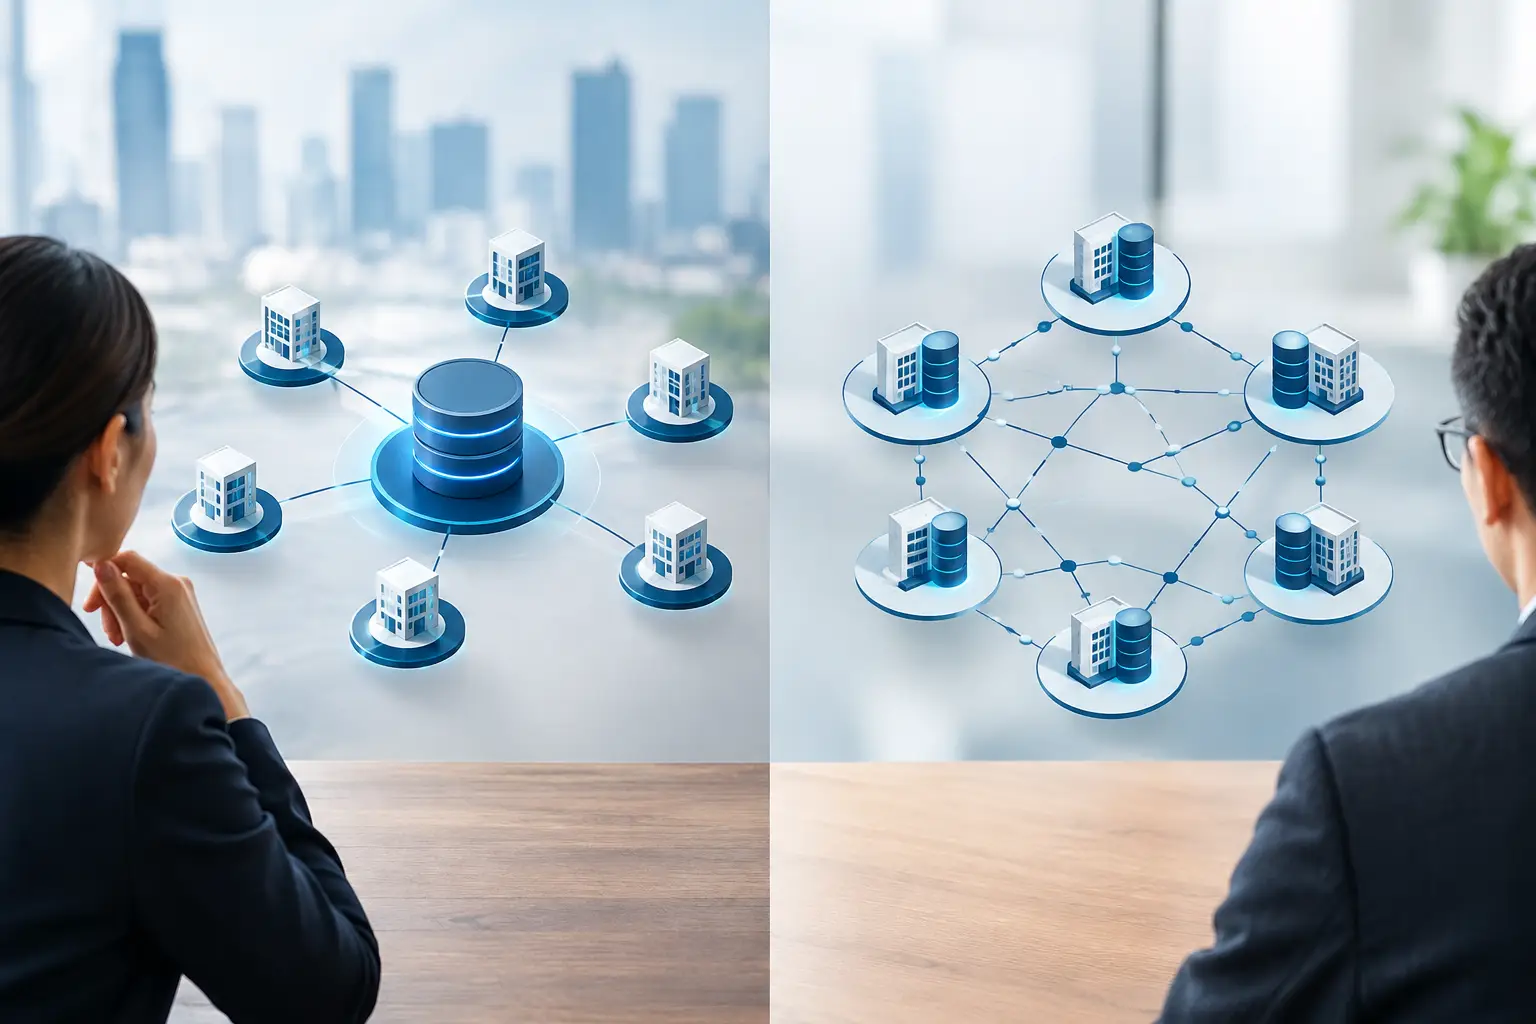
A Malaysian bank can close its monthly regulatory reporting cycle with a centrally governed data platform, yet still depend on finance, risk, and operations teams to interpret exceptions and prepare reconciliations. This is where centralized versus federated governance becomes an operating-model decision rather than an architecture debate. The question is not whether control or business autonomy is better. It is how to place each where it produces trusted, repeatable decisions without creating an analytics bottleneck.
For banks, insurers, takaful operators, government agencies, and GLCs, governance must support accountable data use under real conditions: fragmented source systems, sensitive records, changing reporting needs, and teams under pressure to act quickly. A model that looks orderly on an enterprise diagram can fail if it prevents analysts from resolving a claims anomaly, validating a credit-risk assumption, or investigating a payment exception in time.
What centralized versus federated governance actually changes
Centralized governance concentrates decision rights in a corporate data, technology, or risk function. The central team commonly defines enterprise data standards, access policies, reference data, controls, platform patterns, and approval processes. It is particularly effective when the organization needs a common definition of a customer, exposure, policy, or financial measure across many functions.
Federated governance distributes defined responsibilities to domains that create and use data. Finance owns the business rules behind its reporting data product. Risk owns risk metrics and their meaning. Claims, underwriting, procurement, and operations manage their own governed analytical assets within enterprise guardrails. A central authority still exists, but it sets the rules of participation rather than approving every analytical decision.
The practical distinction is accountability. In a centralized model, the enterprise data office often owns both standards and delivery decisions. In a federated model, it owns standards, assurance mechanisms, and shared services, while business domains own the quality and usability of data and analytics closest to their work.
Neither model is inherently more mature. A highly decentralized organization without common controls can create inconsistent figures and unmanaged access. A highly centralized organization can produce reliable data definitions while leaving business teams dependent on lengthy request queues and spreadsheet workarounds.
Why Malaysian regulated enterprises need a hybrid model
Most large Malaysian enterprises require a hybrid approach. Regulatory, security, and platform controls should be centrally enforced, while data meaning, workflow logic, and priority use cases should sit closer to the business domain.
For a financial institution, central control should typically cover identity and access management, data classification, retention rules, audit logging, approved data-sharing patterns, lineage expectations, and common reference data. These controls help support obligations under applicable Bank Negara Malaysia policy documents, internal risk policies, and the Personal Data Protection Act 2010. They do not remove the need for each institution to interpret its own obligations, risk appetite, and control environment.
Federated ownership is more suitable for the rules that require operational context. A finance team can validate why an account is excluded from a reconciliation. A takaful operations team can explain a claims categorization exception. A credit-risk team can test whether a revised segmentation rule produces a defensible result. Central teams should not become the permanent translators of every business question.
The same principle applies to public-sector and GLC environments. A central data platform team may establish shared security, metadata, and interoperability standards, while individual agencies or business units remain accountable for the accuracy and proper use of the data they publish. This is especially relevant where data is sensitive, jurisdictional requirements matter, and reporting definitions differ by mandate.
The danger of centralizing every workflow
Centralization often begins as a sensible response to inconsistent spreadsheets, duplicated data extracts, and uncontrolled reporting. The risk appears when every workflow change, dataset request, or analytical output requires central intervention. Business teams then export data into local files or develop ungoverned alternatives to meet deadlines.
That is not a failure of self-service analytics. It is a failure to provide governed paths for self-service work. The organization retains formal control but loses visibility into how decisions are actually being made.
The danger of federation without enforceable standards
Federation fails for the opposite reason. Teams may publish similar metrics with different logic, maintain overlapping customer datasets, or permit analytical workflows to move sensitive data outside approved environments. A group-level management report can then become an exercise in reconciling definitions rather than managing performance.
Federation works only when local autonomy is paired with enterprise standards that are specific, testable, and operationally enforced.
Governance for Alteryx One and analytics automation
Alteryx One can be a practical layer in this hybrid model because it allows business analysts and technical teams to build, document, automate, and share analytical workflows. Yet analytics automation should not be confused with governance. Automating an unclear process only produces unclear outputs faster.
A centralized analytics engineering function can define approved connection patterns, credential handling, workspace conventions, workflow promotion practices, reusable macros or components, and minimum documentation requirements. It can also establish which data sources are certified for regulatory reporting, risk analysis, or executive decision support.
Within those boundaries, federated domain teams can build and maintain workflows for high-value processes. Examples include finance reconciliation, credit portfolio monitoring, fraud case preparation, claims exception analysis, actuarial data preparation, procurement controls, and internal audit testing. The domain team remains accountable for business rules and outcome validation. The central team remains accountable for the platform, shared controls, and enterprise integration.
This arrangement is stronger than asking a central data team to build every workflow or allowing every department to create disconnected automations. It creates a governed delivery model where reusable assets can be reviewed, promoted, and operated with clear ownership.
AI-assisted capabilities require an additional layer of discipline. Features such as Ask Alteryx, Alteryx Agents, Agent Studio, Skills, the AI Tool Palette, and MCP Server should be assessed against the organization’s licensed edition, enabled capabilities, data-access model, and internal AI controls. Availability and deployment options can vary. For regulated use cases, teams should define which datasets may be used, what human review is required, how prompts and outputs are retained where necessary, and when an AI-generated recommendation cannot be used as a decision on its own.
The right governance question is not, “Can an agent build this workflow?” It is, “Who is accountable for the source data, analytical logic, approval, and resulting business action?” AI can accelerate workflow development and investigation, but it does not replace accountable ownership.
Build the platform so governance is usable
A modern lakehouse or AI-ready data platform can make hybrid governance more practical. Rather than copying every dataset into departmental silos, organizations can establish governed access to shared data products through controlled interfaces, metadata, and policy-based permissions. Technologies such as Apache Iceberg can support managed table patterns across evolving data estates, while query and integration layers can help teams access data without multiplying unmanaged extracts.
The architecture should distinguish between centrally managed foundational data and domain-managed analytical products. Foundational data may include customer, account, policy, payment, and organizational reference information. Domain products may include a finance close dataset, a liquidity monitoring view, a claims leakage model input, or a regulatory-reporting preparation workflow.
For each product, document the owner, purpose, source systems, quality checks, classification, approved consumers, refresh expectations, and change process. This may sound administrative, but it turns governance into evidence that can be reviewed by audit, risk, compliance, and platform teams.
Tableau and similar decision-intelligence tools also need a place in the model. Central teams should define certified semantic definitions and access controls for enterprise dashboards. Functional teams should retain the ability to investigate operational questions, provided they work from governed data products and understand the limits of the analysis. A visually polished dashboard is not authoritative merely because it is published.
A practical decision framework for executives
Start by mapping decisions, not systems. Identify decisions that must have one enterprise definition, such as group financial performance, regulatory exposure, customer identity, or capital-related measures. These require central standards and stronger assurance. Then identify decisions where local expertise determines value, such as claims triage, branch operations, underwriting analysis, or audit testing. These are candidates for federated delivery within common controls.
Next, define decision rights in plain language. The central team should know what it approves, what it enables, and what it monitors. Domain leaders should know which data products and workflows they own, how changes are tested, and when escalation is required. If these responsibilities cannot be stated clearly, the governance model will remain theoretical.
Finally, measure behavior rather than policy volume. Track use of certified data products, workflow reuse, exception rates, time taken to approve access or changes, unresolved data-quality issues, and the proportion of critical reports with named owners. These indicators show whether governance is enabling trustworthy work or merely adding gates.
The most effective model is rarely fully centralized or fully federated. It is a deliberate operating design: centralize the controls that protect the enterprise, federate the expertise that improves decisions, and make both visible in the platforms people use every day.